Friday, June 10, 2011

Internet Censorship


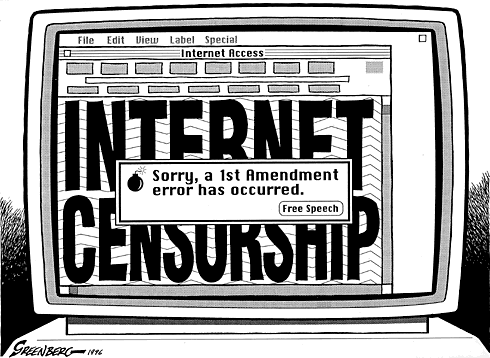
Internet Censorship is becoming a big topic on the web over the last few years. More and more, governments are trying to gain control of the internet, and monitor or censor what their citizens can view, and do on the web. 

The Turkish government has blocked quite a few websites and blogs as of late, and a filtering system is in the making, that may possibly go live on the 22nd of August. This filtering system will make it possible for the government to keep logs of every individual user's activity. As to why or how the system is being put into place, no one really knows. This filter however is an invasion of privacy, as noted by a group of hackers known as "Anonymous". In protest to this recent announcement, they took down Turkey’s Telecommunications Communication Presidency (TIB) which [at the time of this article having been written] is still down.


"Anonymous" and many other hackers have taken to attacking government websites, and other acts of the sort to protest the censorship that is constantly rising in many countries, and they are gaining notice.

Recently, the Protect IP Act has been under the spotlight in the United States, as it passed the Senate Judiciary Committee unanimously. If passed, this bill would give authorities the right to legitimately seize any domain name they deem to be facilitating copyright infringement. The bill, also however, states that if a domain is not registered or controlled by a U.S. company, the authorities can also order search engines to take it completely out of their search results, have ISPs block it, and order the ad-networks (that fund the sites operations in most cases) along with the payment processors for said sites to stop providing their services to the site being blocked.

This new bill is targeting mostly "pirates", and those who distribute copyrighted goods over torrent trackers. While this is all fine and dandy, there are more circumstances to be noted with this idea.

One of the more important notable problems that will arise is the fact that not all torrent trackers are used for illegal sharing. In fact, there are many torrents out on the web right now that are perfectly legal. Many webmasters, individuals, and even companies have taken to using the peer to peer technology that took off in the early 2000's to share their freeware programs, and many other free creations of their own, along with other non-copyrighted materials.

Another important consideration to be made is, if this bill does pass, and the government gets the right to being censoring these domains, that might make way for them to grow with their censorship. This bill is already walking a fine line on infringing rights in The First Amendment [despite it's main alleged intent being to combat piracy].

What is your opinion?
Feel free to share them in a comment below, or discuss it on the forums!

Thursday, May 5, 2011

Walk Into A Business... On Your Web Browser!


So far, Google Maps and Google Earth have proven to be some of the most innovative tools out there for finding directions, searching a location, education, and general fun. When Google added "Street View" to those two services, it allowed the user to see first hand everything 360 degrees from a point on a road of their choosing, and jump from point to point, as if they were walking along the road.

Today, at the Social-Loco Conference in San Francisco, Marissa Mayer [Vice President of Google Maps & Location] announced a new feature that will allow users to see inside of local businesses and buildings from their browser as well, just like Street View! With the use of this technology, users will be able to look around inside of a local restaurant before going to eat there, or look around the inside of a business before a visit.

So, when can we expect this new feature?

It will be available in the United States, Australia, New Zealand, and Canada this coming week! It will be available in other countries in a month or so as well.

Monday, April 11, 2011

Commodore 64 Re-Released!

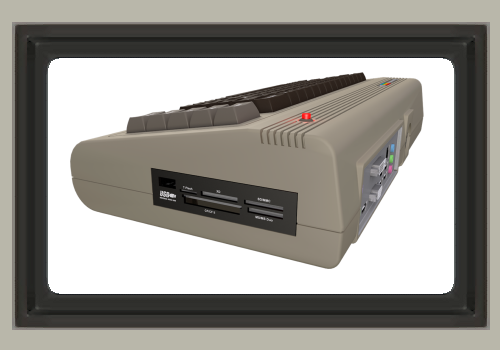
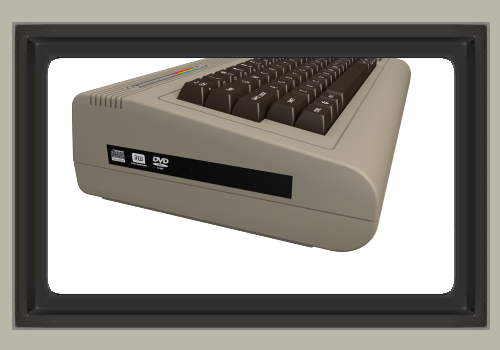
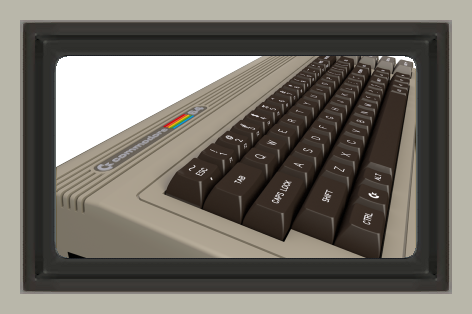
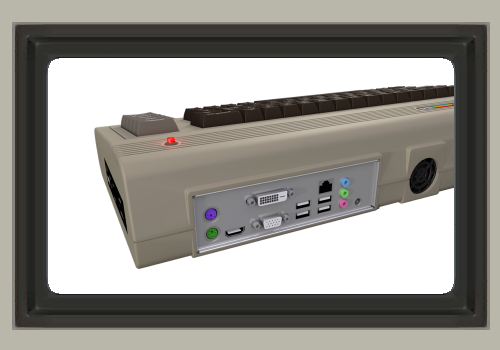
Commodore USA has recently developed and released a re-make of the old-school Commodore system. The system has been designed with some new 21st century features in mind, such as a DVD/RW drive, or even a Blu-Ray drive [depending on which configuration you order], and also a multi-card reader!


The new system currently comes bundled with the Ubuntu 10.04 LTS Operating System, and the Commodore 64 OS that is currently in development for the system will be mailed to the buyer as soon as it becomes available. The system contains a modern mini-ITX PC motherboard, with a Dual Core 525 Atom processor and the latest NVidia Ion2 graphics chipset.


For more information on the new system, click here.

To look at the different configurations available, or to look into ordering one, click here.

Friday, April 8, 2011

Real Snail Mail: E-mails Delivered At The Speed of A Snail


You may have heard someone refer to their "snail mail" before, as they patiently waited for an e-mail to come through, but that was just a nickname. The folks down at boredomresearch took the phrase a bit too literally, and have created the internet's first ever E-mail service run by snails. 

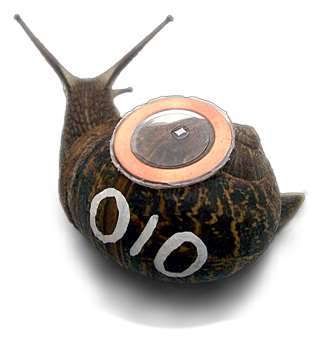
At RealSnailMail, when you send a message, the message is immediately sent to their servers, and assigned a snail. Once assigned, the message is transfered over into a small memory unit attached to the back of the snail via a circuit and antennae. The Snail will be on the receiving side of the enclosure when the message is assigned to it, and once the message is copied over, the snail is released. Once it reaches the other side of the enclosure, the mail is transferred back to the servers, and delivered to the recipient; hence the speed of a snail.


The project has been an educational project to inspire creative minds to think beyond the norm in regards to technology. A good portion of the snails were collected by the children from Castle Hill Community Primary School in Folkestone, and the drawings from the children were used on the Snail Profile Page. This is definitely one of the more creative and funny projects I have seen in technology to date.

Wednesday, April 6, 2011

"Please tap your phone here to pay, sir."

With today's technology making a move towards mobility, and the market for smartphones growing everyday, cellphones are gaining new features, updates, and models at a higher rate than ever before. Apps are being developed everyday with new useful, entertaining, or even silly purposes. With all of these mobile technological advances, the promise of a new standard that may be implemented in the near future has revealed its-self; mobile payments. Not mobile payments as in buying something over an eBay app on your iPhone, and paying for it using PayPal over your 3G connection, but as in paying for something at a gas station or restaurant.


Yes, mobile phones are now looking to gain the technology to replace Credit and Debit cards!

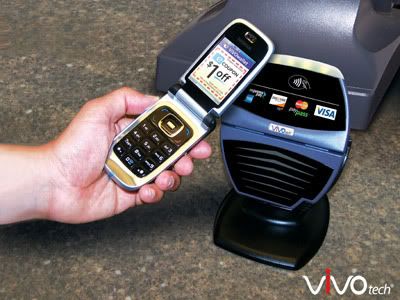
Using a technology known as N.F.C. (Near Field Communication), the phone would be able to send a short-range wireless signal to the N.F.C. reader, which would then process the payment. The chip designed to send the N.F.C. signals are being designed by Qualcomm, a well known company that innovates in Wireless and Mobile technology. If you have a newer phone, and look on the back cover, there's a good chance you'll see the name Qualcomm etched right above "3G CDMA".

When can we expect to see this technology emerge? There is no official date, only the news that it is in the works; thus it may be some time before we will see it first hand. Right now, both Apple and Google are planning to develop and incorporate the technology into the iPhone, and Android devices.

Monday, March 14, 2011

How To Avoid Mal-ware On Your Android Phone


Most who own an Android phone may have recently seen in the news that new malware is appearing, targeting Android users. Google's App market for Android phones allows for developers to publish their newly designed android apps without having to be reviewed first, [unlike Apple's app store]. This has opened a lot of windows for developers, as well as a new one for hackers.

A new scare recently came up known as the "DroidDream" Trojan. Certain Apps were pirated, copied, and then re-constructed with malicious code within them, then put back on the Android market with similar names to the originals. If a user installed one of these apps mistakenly, once installed, the code would take over the user's phone, basically turning it into a paperweight [or staying hidden in some cases instead], while allowing the developer of the app to access all of the information on it, and take full control.

Google has since restored the effected phones to working order, and patched them to be immune if exposed to the Trojan once more. Also, Google removed the apps from the app store. This should serve Android users as a reminder that things like this can happen if you're not careful. Similar threats are quite possible in the future.

Here are some simple tips you can use to make sure you do not fall prey to malicious apps!


1) Check the name of the developer

If you're not sure, a surefire way to find out if the developer you're downloading from is legitimate or not is to check their name. If they have a name like "Iam21090402" or "grwowl2010" for example, there's a good chance the app you're looking at could be malware.


2) Check the description and screenshots

Another way to know whether or not the developer is trusted is to check the screenshots, and description. In the recent string of malware that was put on the store, the screenshots were simply pictures of the logo used for the app, instead of an actual screenshot of the interface of the app. Also, if the description doesn't look legitimate, or is non-existent, you will want to double-check on the app's credibility.


3) Research it

If you're not sure if the app is safe, and have tried both of the previous steps, another measure you can take is to look it up online, by searching it on Google, or otherwise on the internet using your computer. Read some user reviews, and see what people had to say about it.


4) Download latest Android OS updates as soon as you know them to be available


Patches, and OS updates are extremely important, as aside from fixing glitches and issues, they also address security vulnerabilities. Having the latest Android OS is a good way to make sure you're up to speed and protected from all of the latest malware app threats.

----

When installing an app, the user has to choose to install it before it will install. This goes for all apps, and therefore for the malware to get onto your phone, you will have to allow it's installation by mistake. That's why these steps will definitely come in handy when trying to determine what is safe, and what isn't on the app store.

Also, if you're uncertain of the integrity of an app, feel free to contact us on twitter, by tweeting @CompsultInc with the name of the app, or via direct message, and we will gladly look into it for you!

Thursday, March 10, 2011

Bluetooth Jacking


Something unknown to most, that has in fact been an epidemic for quite sometime among hackers, technological pranksters, and people of the like, is Bluetooth Jacking. You may be wondering what is meant by this? What exactly is Bluetooth Jacking? What does it involve? Fear not! Your questions are about to be answered.

Bluetooth Jacking is a form of hacking that takes place over Bluetooth. It's primary targets are mobile phones, and smartphones. It has been around since the mid 2000's, and has been popular amongst hackers across the globe.

Bluetooth Jacking is a technique that involves exploiting vulnerabilities in Bluetooth devices to get into them, such as mobile phones, smartphones, etc. Bluetooth is a small range network type, primarily used for headsets, file transfer, and other phone-related devices/functions. It operates over low power radio waves, which can range up to 30 yards in signal. The frequency Bluetooth operates is known as the ISM band. 

Bluetooth technology has stayed the same over time for the most part, therefore, the security has not changed much either. Using a computer with a functioning Bluetooth signal output, hackers can use custom designed software, or tools from their arsenal to hack into your phone as soon as it is discovered. Typically sitting in an airport, coffee shop, or other local, heavily occupied area, they'll set to work. Once in, they can use your phone to do a various number of things. They can make calls, send SMS Messages, access the web, and even pull your contact list from your phone, getting the information of anyone on your phone that you have entered.

While this may seem frightening, there is one surefire way to avoid this happening to you. If you don't use it, simply go into your mobile device's settings, and turn off your Bluetooth discovery [which is typically on with most phones].

Here is a video showing you an example of a way hackers can use this exploit to scam you: